Governance and architecture
TOGAF 9 Certified · COBIT · ITIL v3 and v4 · ISO/IEC 27001, 27005, 22301
Twenty years of governance practice, from ITIL to AI.
The same five activities, from steering the IS to governing AI.
| Activity | IS | IT | AI |
|---|---|---|---|
| Assess | COBIT maturity, IS mapping | ITIL, ISO 20000, ISO 27001 audits | AI readiness, ISO 42001 maturity |
| Design | Master plan, RACI, PMO | Processes, SLAs, service catalogue | AI policy, register, risk assessment |
| Deploy | Portfolio tools, change management | ServiceNow, GLPI, AIOps | MyAI, agents, AI Process |
| Audit | Governance review | Mock audits 20000 and 27001 | Mock audit 42001 |
| Train | COBIT, project management | ITIL 4, ISO 27001 | ISO 42001, AI literacy |
The same management system, from steering the IS to governing AI.
Business–IT alignment, master plan, project portfolio, roles and responsibilities
Service processes, SLAs, information security, continual improvement
AI policy, use-case register, risk assessment, human oversight, data sovereignty
What our consultants hold today.
TOGAF 9 Certified · COBIT · ITIL v3 and v4 · ISO/IEC 27001, 27005, 22301
3 × PMP · PRINCE2 Foundation · Scrum Master · Lean Six Sigma Black Belt
2 × Microsoft Certified Trainer · 2 × Azure Solutions Architect Expert · MCSE, MCSA
Azure Security Engineer · Fortinet Certified Professional · CCNA Security · Power BI, Python
ISO/IEC 42001 certification in progress.
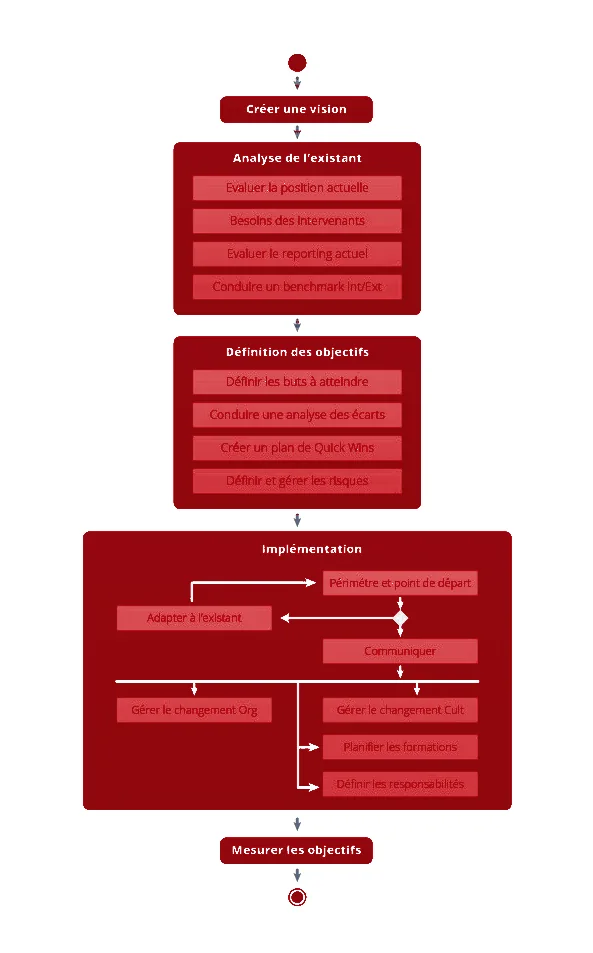
Each phase closes on a governance gate.
Workshops, as-is analysis, maturity scoring
Gap analysis and prioritiesTarget processes, roles, policies, roadmap
Agreed roadmap and process guidesSet-up, pilot, training, knowledge transfer
Processes in operation, teams autonomousKPIs, reviews, mock audits
Continual improvement plan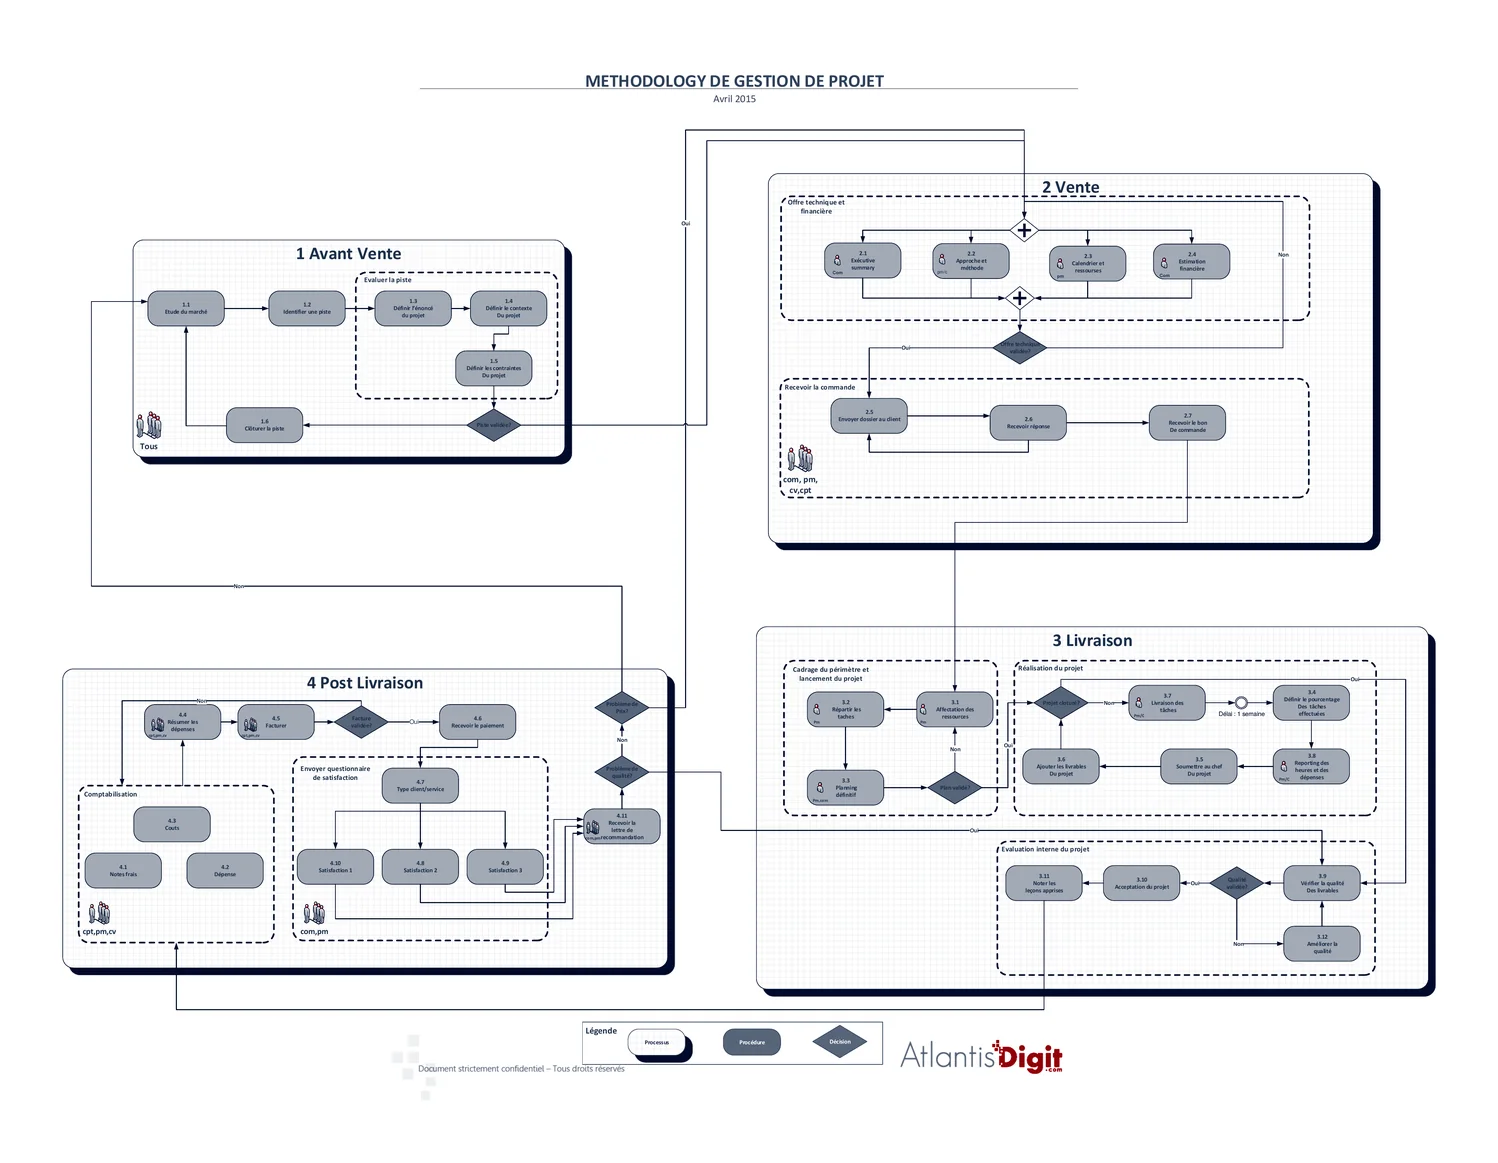
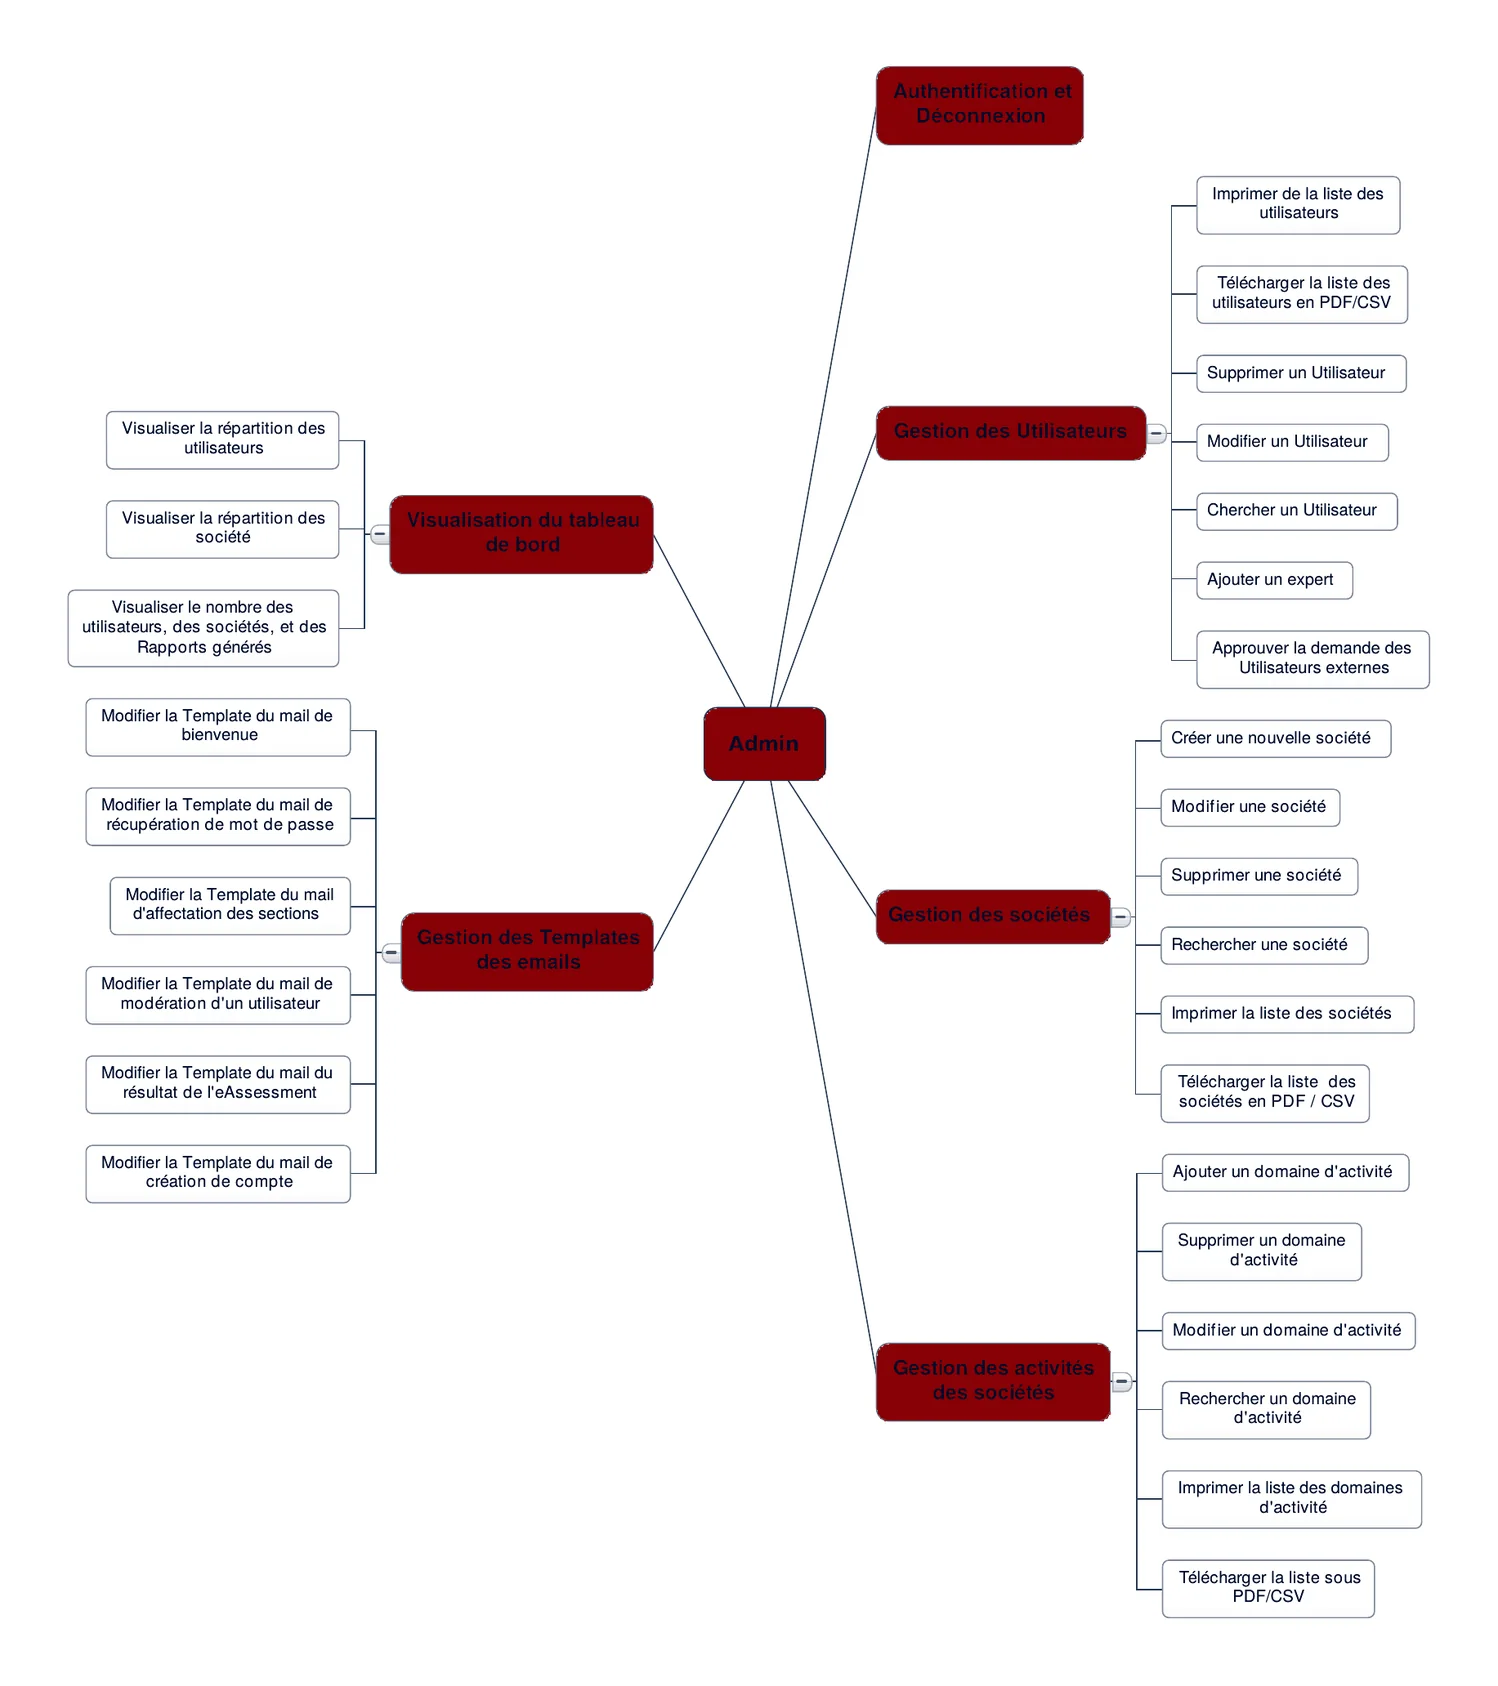
Three pieces from governance and change management engagements.